How CostGlass accesses your data
Security and data ingestion architecture: how CostGlass reads multi-cloud billing and telemetry through read-only roles and least-privilege permissions.
How CostGlass accesses your data
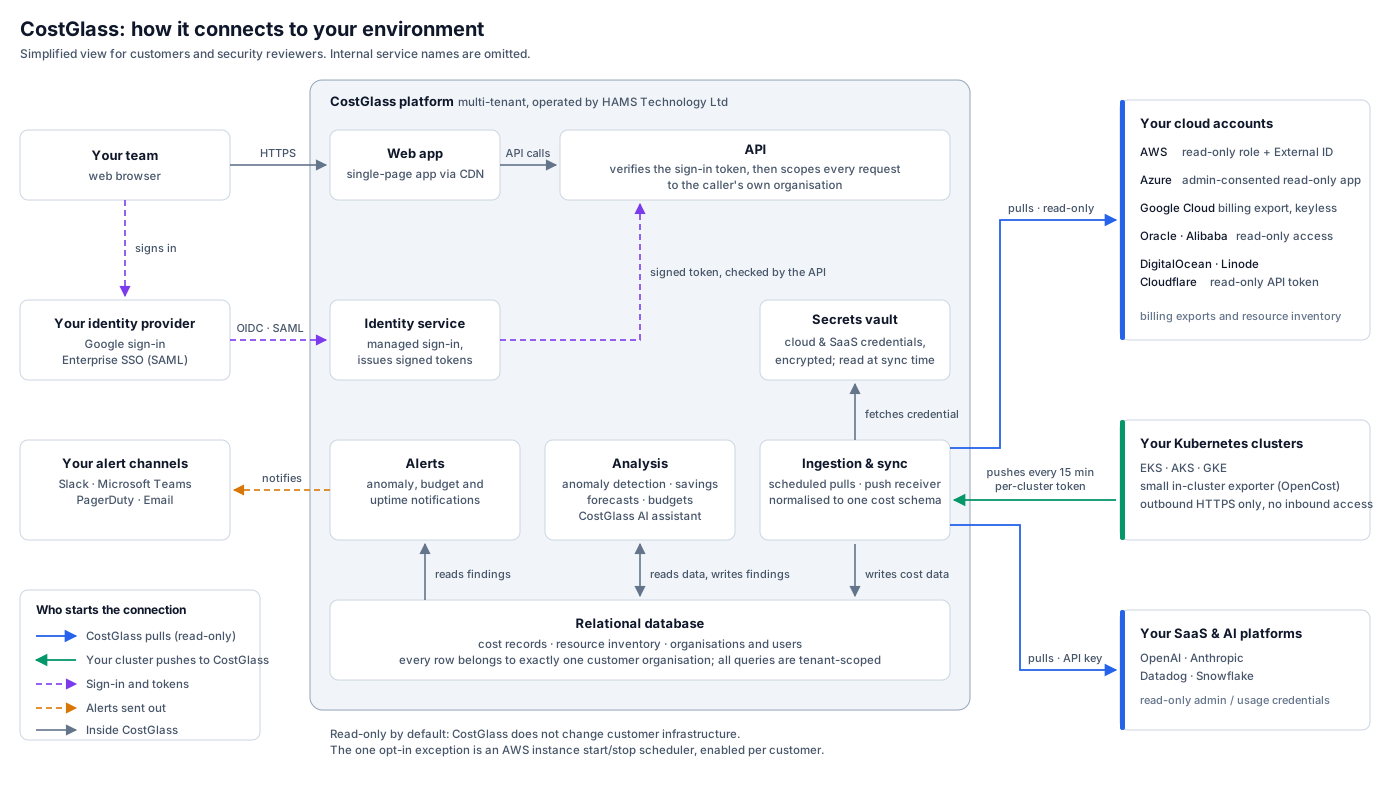
This is the page to send to whoever has to approve us. It covers exactly what CostGlass can reach in your accounts, how the access is authenticated, where the resulting data is stored, and how you revoke it. The short version: read-only access you create yourself, temporary credentials that expire hourly, and data held in the region you choose.
The policy grants cost and billing reads plus Describe and Listactions. There is no Create, Delete, Put or Modify anywhere in it, so CostGlass cannot alter or destroy anything — the one exception being the instance scheduler, which you enable deliberately.
The trust policy requires an exact sts:ExternalId match as well as the CostGlass account ID. Without it, anyone who learned your role ARN could ask AWS to assume it through us — the classic confused-deputy problem. With it, a request that does not carry your value is refused by AWS before it reaches your account.
Choose 🇬🇧 London (eu-west-2) or 🇩🇪 Frankfurt (eu-central-1) when you sign up. Your data is stored and processed there and does not leave that jurisdiction.
The Kubernetes exporter and SaaS collectors send data outward over HTTPS. Nothing dials in to your network: no inbound firewall rule, no public endpoint, no listening port on your side.
CostGlass authenticates to your AWS environment using short-lived AWS STS session tokens. The role trust policy mandates both the CostGlass Production Account ID and your unique tenant External ID: